The term, explained
What is runtime authorization for AI agents?
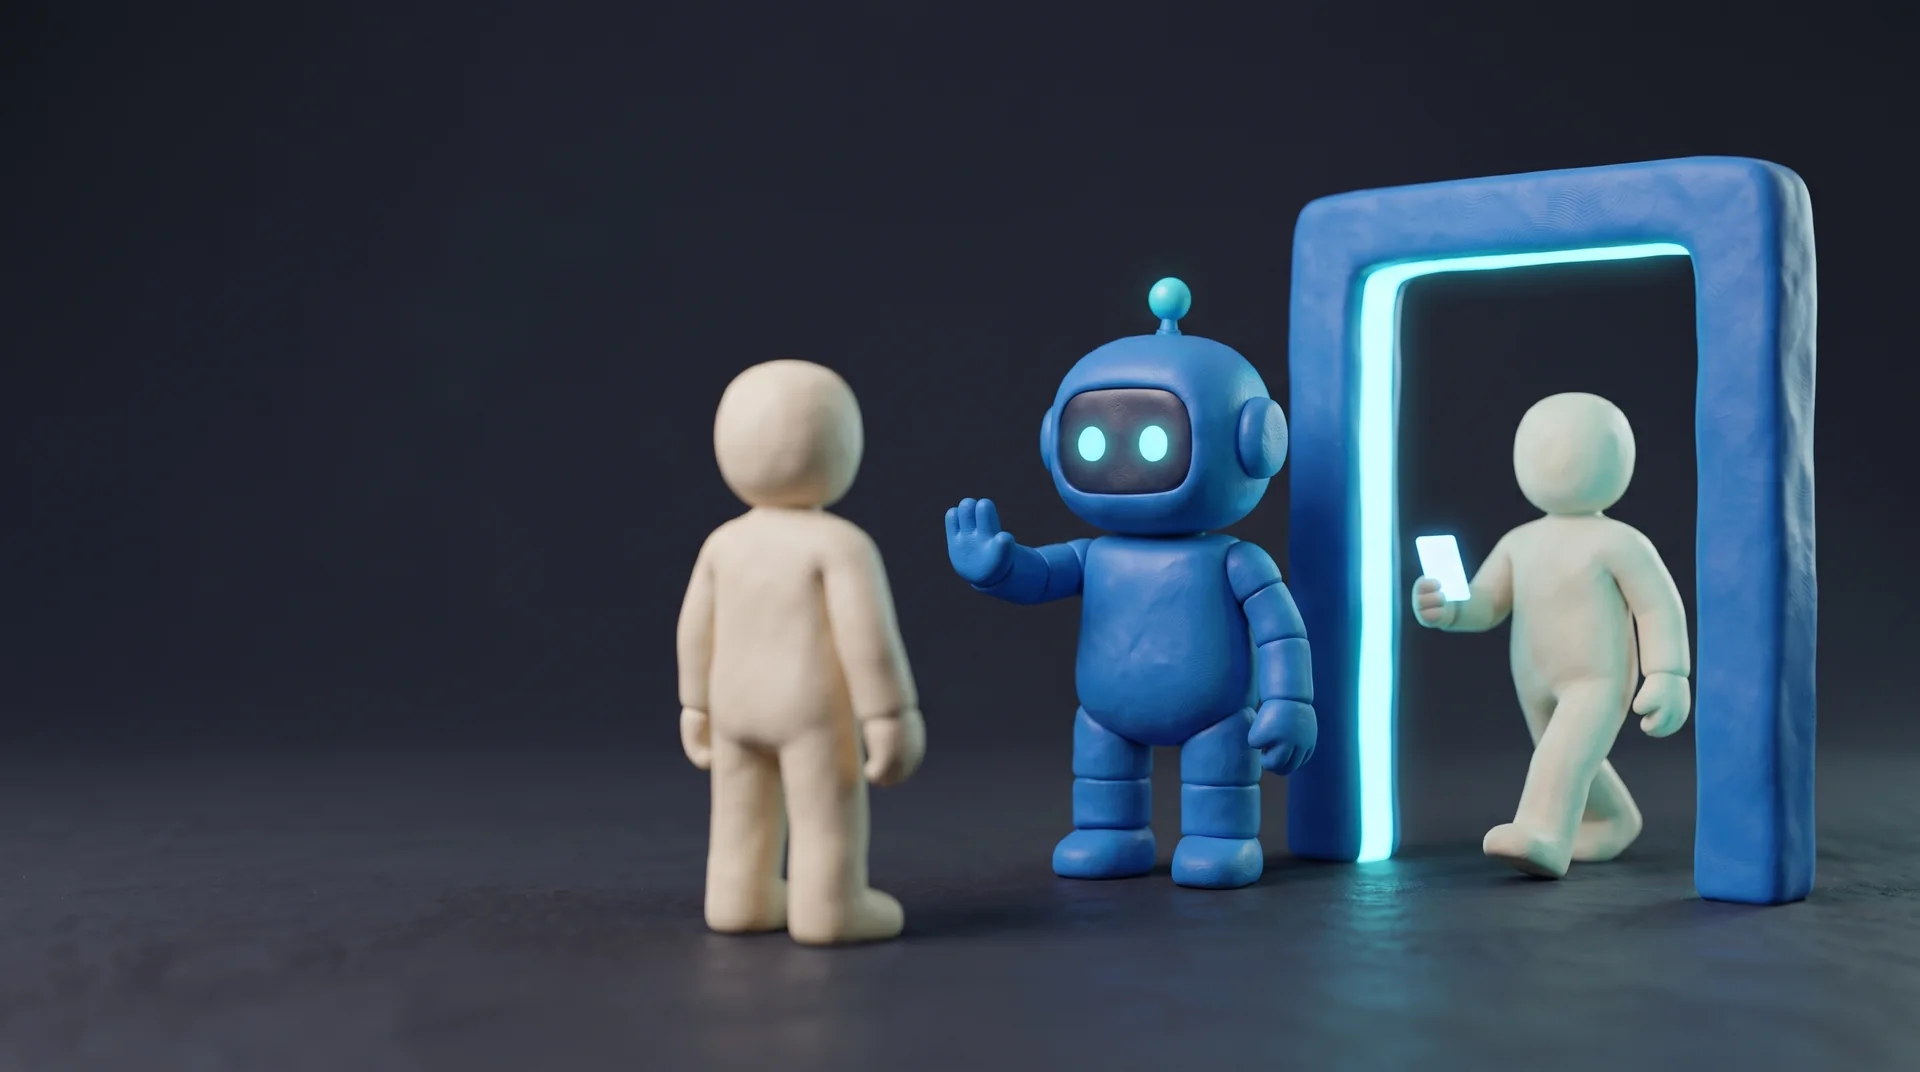
Runtime authorization is the decision, made at the moment an AI agent tries to act, about whether that one action may go ahead. Each consequential action is checked before it executes and is allowed, held for human approval, or blocked. The decision is recorded, so it can be shown later.
AI Acts. Crelis Decides. · Runtime authorization for AI agents
- When
- Before the action executes
- Outcome
- Allowed, needs approval, or blocked
- Proof
- A short-lived execution visa
- Record
- Tamper-evident evidence
Why it exists
Signed in is not the same as allowed
An AI agent that has signed in has shown who it is. It has not shown that the next thing it wants to do should happen.
Being authenticated is not the same as being permitted to do the thing.
Runtime authorization asks the second question, once for each consequential action, at the moment the agent attempts it.
How it differs
Five controls, five different questions
Each of these is useful. Only one of them decides whether a specific action may happen, before it does.
Control
The question it answers
When it acts
Authentication
Who, or what, is this?
At sign-in
Access control
What is this identity allowed to reach?
When access is granted
Guardrails
Is this conversation safe?
While the model is talking
Logs and traces
What happened?
After the fact
Runtime authorization
May this specific action happen now?
Before the action executes
Guardrails read the conversation; authority governs the act.
What happens to one action
Seven steps, before anything executes
Each consequential action moves through seven steps — request received, inputs evaluated, policy applied, decision (allow, require human approval, escalate, or block), execution visa issued or withheld, visa verified by your endpoint, evidence recorded. Deterministic policy evaluation decides; no AI model makes the final call.
Decision pipeline
Illustrative datastep 7/7
Request received
action: payment.wire
Inputs evaluated
amount · channel · tier
Policy applied
WIRE-HIGH v12
Decision
REQUIRE HUMAN APPROVAL
Execution visa issued/withheld
issued after sign-off
Endpoint verifies visa
signature valid
Evidence recorded
sealed · 0x91f3…aa07
The execution visa
Every authorized action receives an execution visa
When GREENLIGHT authorizes an action, it issues a short-lived, cryptographically signed runtime execution visa — who requested it, exactly what was authorized, the policy decision, and its place in a tamper-evident chain. The endpoint trusts the visa — not the AI.
Before an AI agent acts, check its visa.
Issued on every authorized action
- Bound to one action, one resource, one identity
- Short-lived and single-use by design
- Carries its own audit lineage
- Verified independently of the model that asked
Where it matters
Actions that matter, not every action
Runtime authorization is for the moment an AI agent does something that matters. Everyday read-only work is untouched.
Move money
A payment, a transfer, a refund.
Change a record
An account, a limit, a customer file.
Contact a customer
A message sent in your name.
What regulators point to
Controls at the moment an agent acts
We publish an independent, primary-sourced reference mapping SAFR, NIST AI RMF and EU AI Act requirements to controls at AI-agent execution time. It cites the source documents and implies no endorsement.
If you are evaluating
Questions to ask any vendor
Ask any AI vendor one question: after the agent acts, can you produce the record a regulator would accept. Not a dashboard. A record.
- 01Who makes the final decision: a model, or fixed rules?
- 02What happens to a consequential action if the authority cannot be reached?
- 03Can a past decision be reproduced from its recorded context?
- 04Does a human approval become part of the record?
- 05Does the decision need raw customer data, or only decision metadata?
- 06Does the same control cover agents built on different models and vendors?
FAQ
Runtime authorization, in short answers
The questions people ask about authorizing AI agent actions.
What is runtime authorization for AI agents?
Runtime authorization is the decision, made at the moment an AI agent tries to act, about whether that one action may go ahead. Each consequential action is checked before it executes and is allowed, held for human approval, or blocked. The decision is recorded, so it can be shown later.
How is runtime authorization different from authentication?
Authentication establishes who or what is acting. Runtime authorization decides whether one specific action may happen now. An agent can be correctly signed in and still attempt an action that should wait for approval or be blocked. Being authenticated is not the same as being permitted to do the thing.
Is runtime authorization the same as AI guardrails?
No. Guardrails read the conversation; authority governs the act. A guardrail shapes what a model says. Runtime authorization decides what an agent is allowed to do.
What is AI agent access control?
Access control sets what an identity is allowed to reach. For an AI agent that is a starting point, because the agent chooses its own next step. Runtime authorization adds a decision on each consequential action, at the moment the agent attempts it.
When does an AI agent action need human approval?
When policy calls for it. An authorized reviewer decides with full context, and that sign-off becomes part of the record.
What is an AI agent audit trail?
A record of what each agent attempted and what was decided. Every decision is written to a durable, tamper-evident record, so you can show what was decided and prove it has not been altered since.
Does an AI model make the authorization decision?
No. The final decision is never made by an AI model. It is made by fixed, deterministic rules, so the same request always gets the same answer, and every answer can be explained. AI signals can inform the decision; they can never be the decision.
How do we start without changing our systems?
Day one is SHADOW mode: one small configuration change, nothing else touched, and you immediately see a complete, audit-ready record of each consequential action your AI agents attempt through Crelis, alongside what policy would have said. ADVISORY and ENFORCE are modes you switch on later, per organisation, at your own pace.
Give your agents a green light — safely.
Start in shadow mode on non-production traffic. See every decision GREENLIGHT would have made — before you let it make one.